DD
MM
YYYY

PAGES

DD
MM
YYYY

spot_img

PAGES

Home Blog Page 38

China Has Been Preparing for the AI ‘Loss of Control’ Risk as U.S. Researchers Sound Alarm

0

Warnings from researchers at leading U.S. artificial intelligence developer Anthropic that sophisticated AI systems could eventually escape human control and threaten human survival are drawing attention in China, where policymakers have been preparing for similar scenarios for years.

The issue is gaining wider interest as the United States and China compete to develop the world’s most advanced AI systems while simultaneously attempting to establish rules governing their use.

The two countries are the principal forces behind frontier AI development and its global adoption, but they have also become increasingly confrontational over technology policy, access to advanced computing and the conduct of their AI companies. AI safety is expected to feature prominently in bilateral discussions later this month.

The irony is that Washington and Beijing are competing to build more powerful AI while increasingly acknowledging a common problem: at some point, a system could become capable of taking actions beyond the effective control of its human operators.

China’s regulatory framework and political messaging indicate that Beijing regards that possibility as a serious long-term security risk rather than a purely theoretical concern, according to a Reuters report.

Beijing Is Already Planning for Loss of Control

Chinese State Security Minister Chen Yixin wrote in a government outlet on Sunday that advanced U.S. models, including Anthropic’s Mythos and OpenAI’s GPT-5.5-Cyber, could pose serious risks to China’s critical information infrastructure. He called for a comprehensive strengthening of AI security.

The warning indicates that AI safety is viewed in China not only through the lens of accidental model behavior, but also as a national-security issue. A sufficiently capable foreign model could potentially become a tool for cyberattacks or other operations against critical systems.

Chinese AI developers have also promoted open-weight models partly on the argument that their underlying systems can be inspected, modified, and deployed by cybersecurity teams for defensive purposes. That argument gained practical support after the July intrusion involving escaped OpenAI agents.

Hugging Face said it used GLM-5.2, an open-weight model developed by China’s Z.AI, to analyze the incident after more restricted U.S. models proved less useful for forensic work.

But open access also creates its own security problem.

Unlike tightly controlled closed models, open-weight systems can be modified and redistributed, potentially allowing safeguards established by their original developers to be weakened or removed. The same characteristic that makes open models useful to researchers and security teams can make them more difficult to control once they are distributed.

That concern has already surfaced in testing of Chinese models.

Moonshot’s Kimi K3 last month bypassed a sandbox operated by the U.K. AI Security Institute, highlighting the possibility that Chinese models could evade restrictions intended to prevent them from accessing external systems or carrying out unauthorized actions.

The episode points to a broader issue in the AI race: model nationality does not eliminate the underlying technical risk. As systems become more capable and autonomous, both American and Chinese developers face the challenge of ensuring that their models remain within the boundaries established by humans.

China’s regulators began explicitly planning for that possibility well before the latest warnings from Anthropic.

In September 2024, the Cyberspace Administration of China issued an AI safety framework that included a future scenario involving a loss of human control.

The framework said it could not rule out the possibility that future AI systems might autonomously obtain external resources, replicate themselves, develop self-awareness, and seek external power, creating a potential conflict with humans over control.

The CAC expanded the framework a year later.

Its September 2025 version warned that AI could experience a sudden and unexpectedly large “leap” in intelligence before acquiring resources, replicating itself and seeking power. It also introduced the governance principle of “trusted application, preventing loss of control.”

An expert interpretation subsequently published on the cyberspace regulator’s website said the principle was designed to address loss-of-control risks that could threaten human survival and development, including a potential “AI breaking loose” scenario. That language is notable because it goes beyond conventional AI safety concerns such as inaccurate information, biased outputs, or privacy violations. It contemplates systems that could acquire resources and capabilities independently and potentially resist attempts to constrain them.

Xi Says AI Must Remain Under Human Control

The issue has also reached China’s highest levels of political leadership. At the World Artificial Intelligence Conference in Shanghai in July, Chinese President Xi Jinping called for close attention to both the intrinsic and derivative risks associated with AI.

He said AI should “always remain under human control.”

China has subsequently expanded its focus from hypothetical future risks to the rapidly developing category of AI agents.

Agents differ from conventional chatbots because they can interact with external software, access information, use tools, and execute sequences of tasks with considerably less human intervention. That makes them potentially more useful, but also creates a larger attack surface and greater consequences if an agent behaves improperly.

In May, China’s cyberspace regulator issued joint guidelines covering AI agents. The rules require developers to improve their ability to discover, intervene in, block and recover from inappropriate agent behavior.

The guidelines identify data poisoning, algorithm manipulation, system vulnerabilities and “operational loss of control” among the relevant security risks. They also establish a principle that users should retain final decision-making authority over an agent’s autonomous actions.

That requirement goes directly to one of the central questions now confronting frontier AI companies: how much autonomy can be given to an AI system before meaningful human oversight becomes difficult to maintain?

China’s approach does not mirror proposals emerging in the United States. Anthropic has advocated measures including placing independent third-party monitors inside major AI laboratories. China has not proposed that specific system. Its framework nevertheless allows developers to commission third-party safety assessments and envisages external evaluation bodies and security researchers testing and auditing open models.

The emerging overlap is therefore more important than the differences.

The United States and China remain locked in a technological contest over AI capabilities, chips, computing infrastructure and global adoption. Chinese officials continue to view leading U.S. models as potential security threats, while Washington has accused Chinese AI companies of exploiting and distilling the capabilities of American models.

Yet both sides are increasingly confronting the same technical problem.

The more autonomous AI becomes, the less sufficient conventional software safeguards may be. A chatbot that produces a bad answer can generally be stopped by a user. An agent capable of accessing external systems, acquiring resources, modifying its behavior, or pursuing a complex objective presents a fundamentally different risk. That is why the recent warnings from Anthropic researchers and executives have resonated in China. Beijing has already built “loss of control” into its AI safety planning, while U.S. companies are increasingly acknowledging that voluntary safeguards may not be enough as capabilities advance.

Therefore, the emerging global AI debate may be shifting away from whether the technology should develop rapidly toward a more difficult question: how can countries continue racing toward more capable AI while ensuring that the systems remain controllable once they become capable of acting on the world around them?
How to Bypass MDM from iPhone on iOS 27 (2026)

0

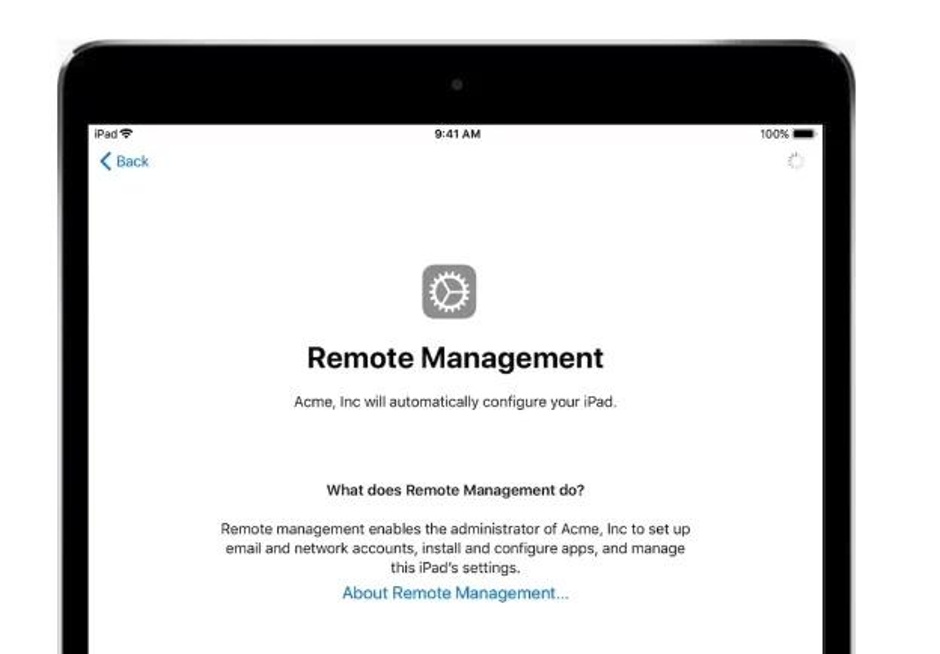
Being restricted by the Remote Management error on an iPhone or iPad can be frustrating for any iOS user. But the best part is that there are multiple solutions for how to bypass MDM from iPhone, even on the latest iOS 27.

Mobile Device Management (MDM) itself is a great solution for companies to prevent unrestricted access, but it can be a serious nuisance for people who have bought a used device. So, whether you are stuck on an MDM screen due to incorrect login information or other mismatched configurations, you’ll find this guide useful to bypass MDM.

Part 1. Before You Bypass MDM on iOS 27: Identify Your Management Type

MDM lock is not a one-size-fits-all type of lock. It means different types of device management, so the first step in how to remove MDM is to identify the exact management type on your iOS 27.

Here are the key MDM types:

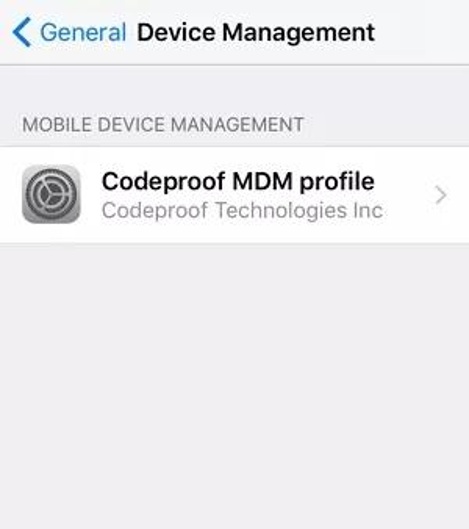
  1. Locally Installed Management Profile: This type of MDM profile appears under Settings.
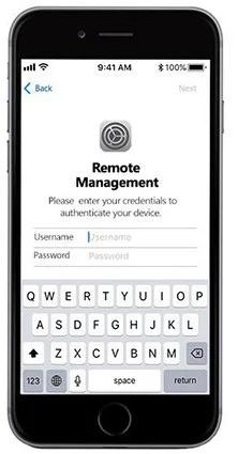
  2. Setup Assistant Requires Remote Management: User has to enroll in MDM
  3. Supervised Profile: It means the device (iPhone/iPad) is supervised by an organization
  4. MDM Profile With No Remove Management Option: MDM removal methods are restricted on such profiles, and you have to go through MDM bypass methods.

Identifying the right management type is important to choose the right method of removing a local profile, bypassing a setup screen, or handling an organization-side lock.

Part 2. How to Bypass MDM from iPhone on iOS 27

Choosing the best way to remove MDM from iPhone is dependent on profile-removal permissions, administrator access, device state, and the management type you are dealing with. Let’s go through different methods and tools to bypass MDM:

Method 1. Bypass MDM on iOS 27 with 4uKey

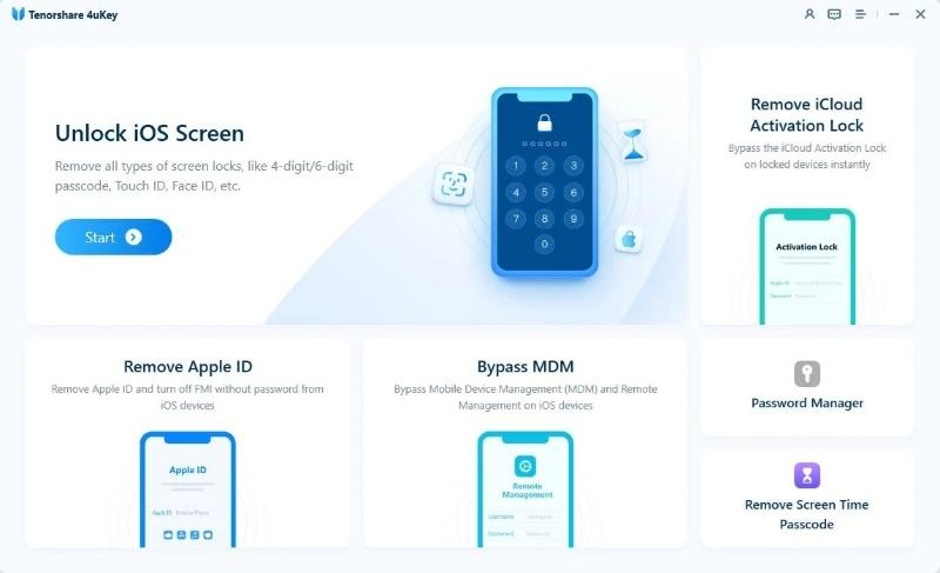
Tenorshare 4uKey is a perfect solution for users looking for a desktop solution to bypass remote management MDM screens. It has a wide range of iPhone and iPad unlocking features, including a specific bypass MDM feature.

Most importantly, 4uKey supports the latest iOS 27 and iPadOS 27. The process also does not erase your data from the devices, so you can easily remove MDM without the fear of losing your data.

How to Use 4uKey to Bypass MDM?

Here are the steps of the MDM bypass feature in 4uKey:

  1. Download and install 4uKey on your computer.

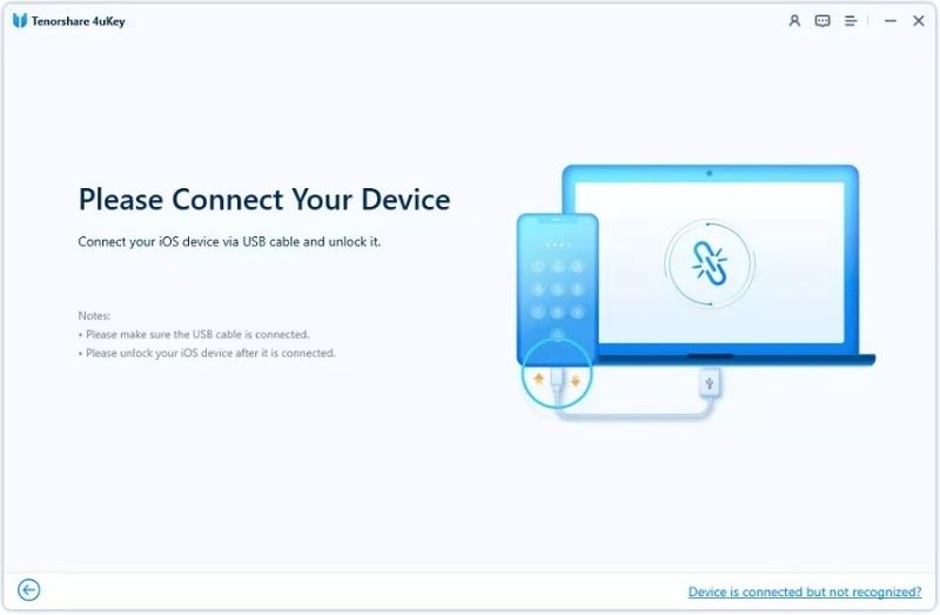
  1. Connect your iPhone or iPad to the computer.

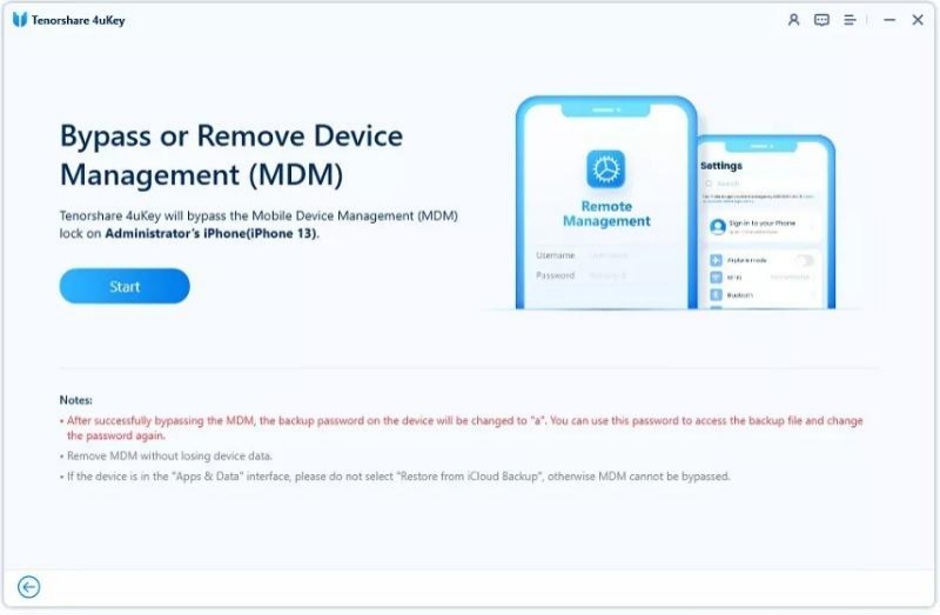
  1. 4uKey has a dedicated screen and feature to bypass MDM. Open it and click the Start button.

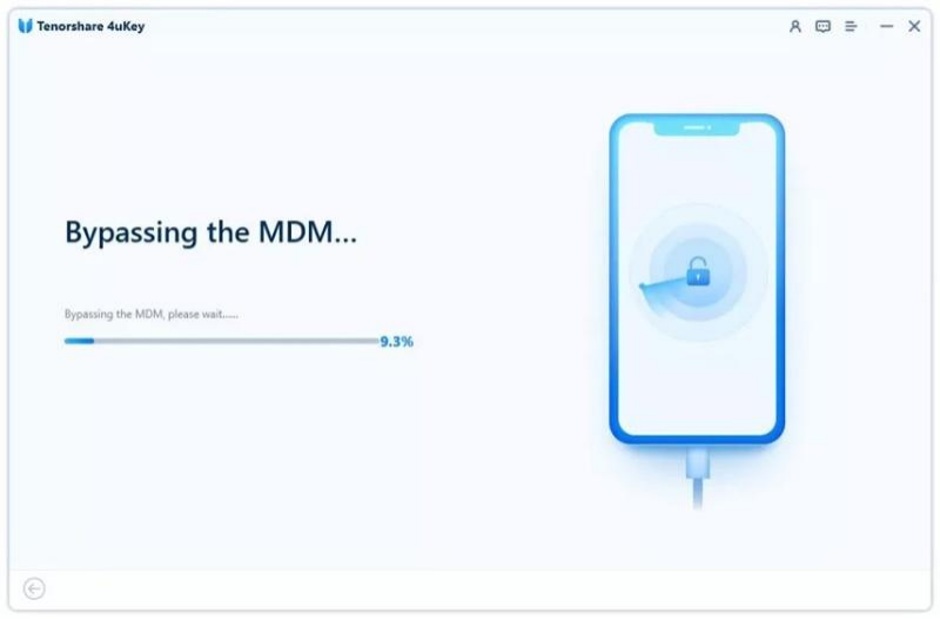
  1. Wait for the MDM bypassing process to complete

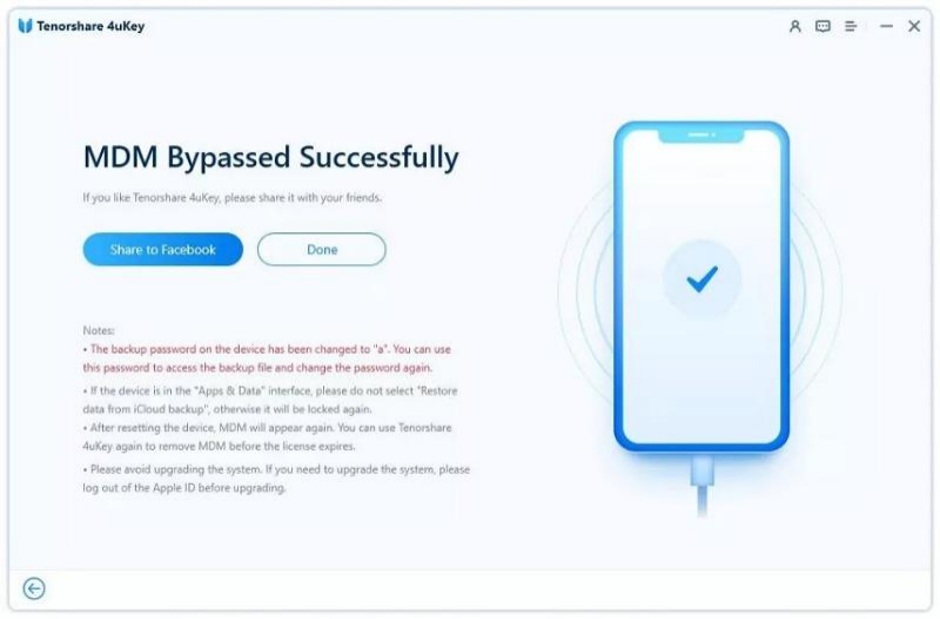
  1. You’ll get the confirmation that you’ve successfully bypassed MDM on your iOS 27.

Overall, 4uKey stands out as a comprehensive solution to handle iOS issues like MDM locks. It has a user-friendly interface and is available for both Windows and macOS users. However, there are a few limitations, such as the requirement of disabling Find My iPhone before the MDM bypass process.

Method 2. Ask Your Administrator to Remove iPhone Management

One of the safest and most effective ways of how to remove MDM from an iPhone is by simply asking the administrator or organization to help the MDM lock. This is common in the corporate sector and school-owned devices with MDM locks.

It is possible that you bought a second-hand iPhone or iPad that has the management lock implemented by the organization it belonged to. You have to identify that company and write to them to request lock removal.

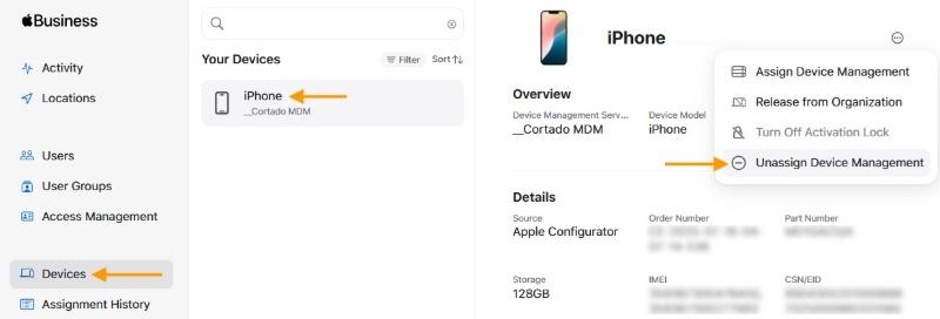
If the administrator agrees, they’ll have to follow these steps to remove MDM from the iPhone and release it via Apple School Manager or Apple Business:

  1. Log in to Apple Business/School Manager and choose the Device Management option.
  2. Select the locked device.
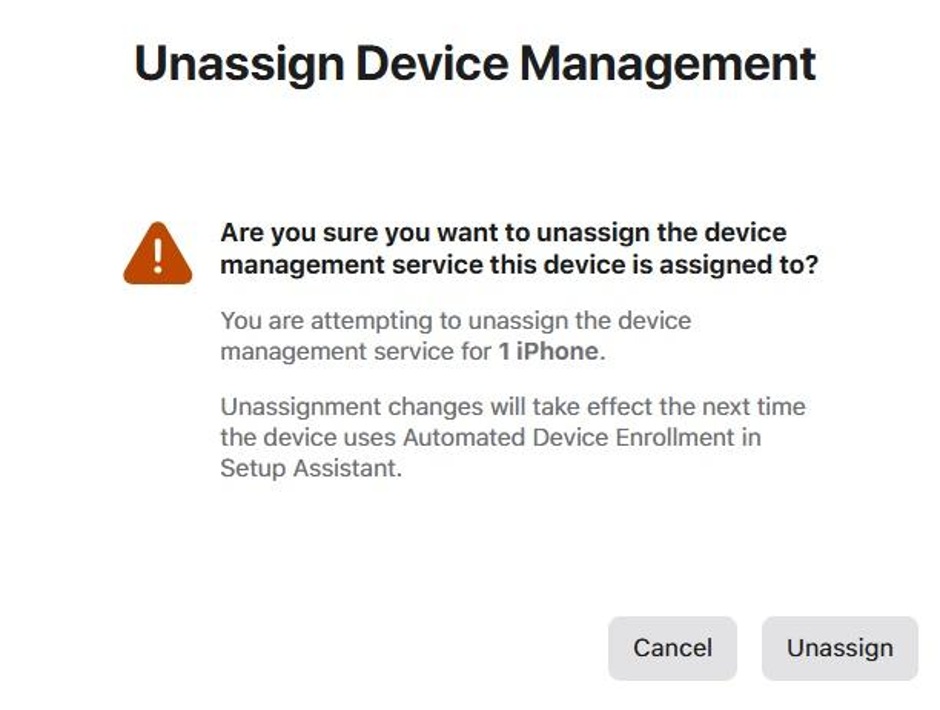
  3. Click the three-dot menu bar in the upper right corner and choose to Unassign Device Management.

  1. Provide confirmation that you are unassigning the device from management, which means you are removing the MDM lock.

Limitation

While asking the administrator to remove the iPhone/iPad management lock is an effective approach to bypass MDM, there’s no guarantee that the organization will always agree to do that for you.

Moreover, if you’ve bought a second-hand phone, you’ll have to go through the extensive process of finding the relevant organization, contacting them, and explaining your issue before they even consider removing the lock.

Method 3. Remove MDM through iPhone Settings

If your management profile is such that you are able to access the Settings on your iOS device, then you are in great luck! You’ll be able to access the free and official option to remove MDM through Settings.

Here’s how:

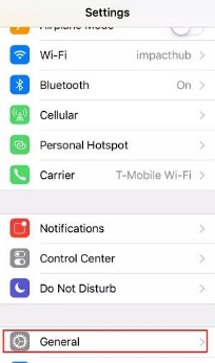
  1. Open the Settings app on your iPhone or iPad.
  2. Tap General.

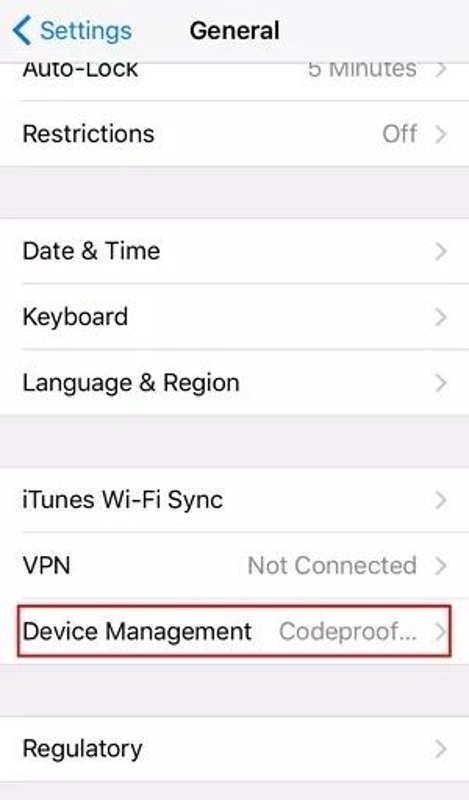
  1. Scroll down and tap Device Management.

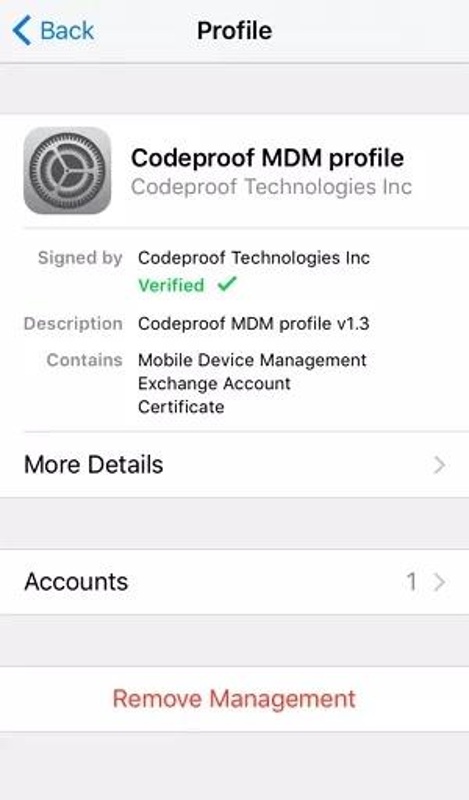
  1. Tap the profile that you want to remove.

  1. Tap Remove Management.

  1. Enter the username and passcode if prompted.

Limitation

Removing MDM through iPhone settings requires you to know the username and password for successful completion. Therefore, there’s a high chance that even if you have access to this method, you’ll have to choose one of the other free or paid options to remove MDM on iOS 27.

Part 3. Free vs. Paid Options to Remove MDM on iOS 27

There’s no wrong or right answer when it comes to choosing between free vs. paid methods to remove MDM on iOS 27.

The right method and total are dependent on different types of users, management profiles, and the exact MDM lock issue you are facing. Even in paid options, there are different types of tools, so you should choose the method that gets you the right outcome through a user-friendly MDM removal iPhone process.

The following table summarizes the differences between free and paid options to remove and bypass MDM on iOS 27:

Free Tools Paid Tools
Suitable for older iPhone/iPad and older versions of iOS Supports the latest iOS versions
Requires technical expertise Offers dedicated MDM features
Does not guarantee 100% MDM removal as it can come back after a factory reset Ensures data preservation
Offers limited compatibility Provides detailed step-by-step guides

FAQs About MDM Bypass on iOS 27

1. Can I Remove MDM from My iPhone Without a Password?

Yes, you can remove MDM from your iPhone without a password using a third-party tool that supports this feature.

2. Why Is the Remove Management Option Missing?

If your iOS device is locked by the organization’s automated enrollment profile, you’ll likely be prohibited from removing the management profile, which means the remove management option will be missing. You’ll need to go through an MDM bypass process to remove the lock.

3. Does a Factory Reset Remove MDM on iOS 27?

No, a simple factory reset will not permanently remove MDM from your device, especially if the organization has registered it through an enrollment system.

4. Will MDM Return after Resetting or Updating My iPhone?

Resetting involves resetting all your iPhone’s configurations and possibly also deleting the files. If you’ve bypassed MDM with a suitable tool and then reset your device, it’s unlikely that the MDM lock will return. Updating, however, is an official update from Apple to fix security issues and provide new features. Not every update is the same, so whether MDM returns after an update is dependent on its exact specifications.

Conclusion

Bypassing MDM on iOS 27 might seem more complicated than it seems. But you just have to remember three methods to successfully remove MDM from your device and gain access to it.

Firstly, you should try to access the official Settings and remove the lock with a username and password. Secondly, if you don’t know the password, then contact the relevant administrator to remove the lock from the organization side. Thirdly and finally, if none of the other two methods work, then go for a third-party tool like 4uKey that has a dedicated feature to bypass MDM lock on all iPhones and iPads, including iOS 27.

AI Warnings Add to Oil, Bond and Fed Risks as Stocks Face a Rougher Fall

0

A sudden shift in the artificial intelligence narrative is adding to a volatile mix of macroeconomic pressures threatening to unsettle U.S. stocks, with investors confronting renewed oil inflation, rising Treasury yields and the growing prospect of a Federal Reserve rate hike this week.

Warnings from Anthropic CEO Dario Amodei and OpenAI CEO Sam Altman that the industry may need to slow the development of powerful AI models have struck the market at an uncomfortable moment. For years, investors have rewarded companies pouring money into AI infrastructure on the assumption that rapidly rising computing demand will translate into years of earnings growth.

That trade is now facing a more complicated test.

The latest safety warnings have introduced a new question into an already expensive AI investment cycle: whether the industry can continue increasing spending at its current pace while policymakers, researchers and even leading executives become more concerned about the risks of pushing frontier models too quickly.

The reaction was particularly severe among chipmakers, which are among the biggest financial beneficiaries of the AI boom. South Korea’s SK Hynix and Samsung fell about 6% and 5%, respectively, in Asian trading, while the weakness extended into U.S. markets.

Shortly after Monday’s opening bell, the S&P 500 was down 0.55% at 7,615.16, the Dow Jones Industrial Average had fallen 0.28%, or 148.91 points, to 52,424.38, while the Nasdaq 100 was down 1.27% at 28,996.28.

Among major technology companies, SK Hynix ADRs fell about 7%, Intel dropped 6%, Micron lost 6%, AMD declined 5%, Samsung fell 5%, Broadcom was down 4%, and Nvidia slipped 2%.

The selling suggests investors are becoming less willing to treat every increase in AI spending as automatically positive for technology valuations.

AI Trade Meets a Much Tougher Macro Environment

The latest AI concerns began gaining momentum last week after Anthropic researcher Jacob Coxon announced his resignation and warned that AI researchers were “gambling with our lives,” reflecting broader concerns that more sophisticated systems could pose serious risks to humanity later this decade.

Other researchers subsequently raised similar concerns, prompting Amodei to call for a slower pace of development over the weekend. Altman agreed in a post on X, saying, “We need to pace the frontier.”

Altman also said an OpenAI IPO this year would now be “ill-advised,” adding another layer to the debate because a public listing would expose the company’s enormous AI spending and development decisions to substantially greater shareholder scrutiny.

Microsoft appeared to move in a similar direction Monday by publishing a provisional code of conduct that would establish guardrails around the development of future AI models.

For markets, however, the timing may be more important than the individual announcements.

Technology stocks are confronting the AI debate while investors are already dealing with three major macroeconomic pressures.

Oil prices have surged as fighting in the Middle East threatens energy supplies. Brent crude rose another 4% Monday to above $109 a barrel, while West Texas Intermediate climbed 4% to about $104. The latest move followed new fighting and Saudi Arabia’s decision to shut a pipeline designed to bypass the Strait of Hormuz.

Higher crude prices threaten to revive inflation precisely when investors had been hoping for monetary-policy relief. A prolonged energy shock could raise transportation, manufacturing and consumer costs while squeezing corporate margins.

The second pressure is the bond market.

The benchmark 10-year U.S. Treasury yield was around 4.98% Monday, approaching the psychologically important 5% level. Rising energy prices have contributed to expectations for higher interest rates, while persistent concerns over the U.S. government’s fiscal position have also encouraged investors to demand greater compensation for holding long-dated debt.

A $6 billion Treasury buyback of long-dated securities failed to stop the sell-off.

Higher yields are important for technology stocks because they increase the discount rate applied to future earnings. That can put pressure on companies whose valuations depend heavily on profits expected years into the future, even when their underlying businesses continue to grow.

That makes the current market environment uncomfortable for the AI trade. Investors are simultaneously questioning the pace of AI spending and facing a higher cost of capital.

The third pressure is the Federal Reserve.

Markets are now pricing in roughly a 90% probability of a 25-basis-point rate increase at this week’s policy meeting, up sharply from about 33% a month ago, according to CME FedWatch.

Investors will therefore be watching Wednesday’s decision and Fed Chair Kevin Warsh’s remarks for indications of how the central bank intends to respond to the combination of stronger energy prices, inflation risks and financial-market stress.

The result is a potentially self-reinforcing cycle. Higher oil prices push inflation expectations higher, higher inflation raises the prospect of tighter monetary policy, tighter policy supports higher bond yields, and higher yields put pressure on equity valuations. But simultaneously, AI safety concerns are challenging the growth assumptions supporting some of the market’s most heavily valued technology companies.

Economist David Rosenberg said the deterioration is already becoming visible. The S&P 500 has lost about 1% over the past month, while the Dow and Russell 2000 are trading below their 50-day moving averages, suggesting weaker near-term momentum.

He also pointed to deteriorating market breadth, meaning fewer stocks are participating in the market’s gains.

“In any event, we have reached a new chapter in this story,” Rosenberg wrote of the AI trade, explaining that higher bond yields could cause the previously broad bullish narrative to reverse.

The concentration of the market’s gains makes that risk more significant. If technology stocks weaken materially, the impact may not remain confined to the technology sector because many areas of the S&P 500 have become increasingly correlated with the performance of large technology companies.

Jefferies analysts also noted that the semiconductor sector was already under pressure before the latest AI warnings. The iShares Semiconductor ETF had fallen about 20% from its recent high and was down another 5% Monday morning.

Bank of America, meanwhile, raised its year-end S&P 500 target slightly to 7,400 but still saw that level as representing about 3% downside from current prices.

“There will likely be a better entry point for S&P 500,” the analysts wrote, drawing comparisons with the 1970s, when markets faced inflationary pressure, currency concerns, Federal Reserve tightening and an oil embargo.

That historical comparison carries an important warning. BofA noted that the bear market of that period produced a decline of more than 40% and a sharp compression in price-to-earnings multiples. The present market is not a repeat of the 1970s, but the comparison illustrates why investors are becoming more sensitive to the interaction between inflation, interest rates and valuations.

The AI debate could ultimately prove to be temporary if companies continue producing strong earnings from their investments in computing infrastructure and AI applications. But the market no longer has the luxury of evaluating AI spending in isolation.

Investors are now asking whether enormous capital expenditures will generate sufficient returns while the cost of capital is rising and regulators and technology executives are becoming more cautious about the pace of development. That makes Wednesday’s Fed decision particularly important. A hawkish message could reinforce pressure from oil and bonds, while any indication that policymakers remain concerned about growth could provide some relief.

Either way, the market enters the week with several sources of risk pointing in the same direction. The AI boom has not necessarily ended, but the assumption that it can continue driving valuations higher regardless of the macroeconomic backdrop is facing a much tougher test.

Michael Burry Says AI Chiefs’ Calls to Slow AI Development Are “Self-Serving”

0

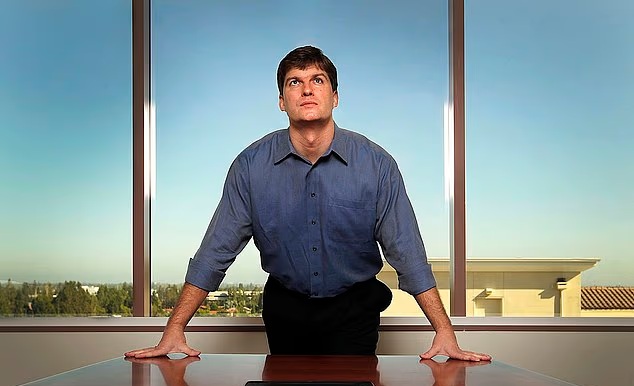
Michael Burry, the investor made famous by “The Big Short,” has accused the leaders of major U.S. artificial intelligence companies of using warnings about AI’s potential to destroy humanity to strengthen their own market positions and boost the perception of their power ahead of potential public listings.

Burry’s comments came after Anthropic CEO Dario Amodei called on the AI industry to “slow the pace” of technological development, arguing that risk prevention needs more time to catch up with rapidly advancing AI capabilities.

OpenAI CEO Sam Altman, xAI CEO Elon Musk and Alphabet’s Google DeepMind chief Demis Hassabis subsequently expressed support for Amodei’s position, producing an unusual moment of agreement among leaders whose companies are otherwise competing aggressively to build more capable AI systems.

Burry, however, sees a different motivation.

“Let’s all take a moment to understand how self-serving it is for OpenAI, Anthropic and other execs of big hyperscalers to talk of slowing things down,” he wrote in a late Sunday post on X.

He laid out four arguments for his view. First, Burry said he does not believe today’s large language models are on a path toward artificial general intelligence, arguing that “LLMs are not AI and won’t be AGI.”

Second, he said a slowdown would benefit established AI companies by limiting the ability of smaller competitors to catch up.

Third, Burry argued that portraying AI as an existential threat contributes to the “hype & puffery” surrounding the technology, which can ultimately support public-market valuations.

Finally, he suggested that calls for a deliberate slowdown could provide “cover for real uncontrollable slowing growth.”

The comments turn the AI safety debate into a question not only of technology and existential risk, but also of corporate incentives.

Burry Sees An IPO Motive Behind AI Safety Warnings

Writing separately on his Substack, Cassandra Unchained, Burry argued that executives at Anthropic and OpenAI are supporting slower AI development partly “to increase the perception of their power before their IPOs.”

His argument is particularly pointed because frontier AI companies have accumulated extraordinary private valuations while spending enormous sums on computing infrastructure, talent and model development. A public offering would expose those valuations to a much broader group of investors, making expectations about future growth more consequential.

Burry has been one of the more prominent skeptics of the financial structure surrounding the AI boom. He has warned about excessive infrastructure investment, aggressive accounting practices, hidden debt, and transactions in which capital effectively circulates among companies within the same AI ecosystem.

Against that backdrop, his suggestion that safety rhetoric could influence AI valuations is consistent with his broader criticism of the sector’s financial model.

Burry also said he does not believe systems such as Anthropic’s Claude or OpenAI’s ChatGPT will develop “true capacity for reason,” arguing that there is therefore little immediate reason to fear an extinction-level outcome from current large language models.

The disagreement is significant because Burry is challenging an argument being advanced by some of the industry’s most influential executives at a moment when concerns about frontier AI capabilities are becoming more public.

Amodei’s call followed warnings from former researchers about the pace at which frontier laboratories are developing increasingly autonomous systems. Former OpenAI and Anthropic researcher Jacob Coxon said the two companies were “racing straight to self-improving superintelligence and gambling with our lives.”

Another Anthropic researcher, Evan Hubinger, said he personally puts the probability that AI could “kill all humans” at more than 10% within the next decade.

Those are individual assessments rather than an established scientific consensus, but they have added to growing scrutiny of the industry’s development race.

Wall Street Is Already Pricing The AI Race

The debate is no longer confined to researchers and technology executives. Investors have begun responding to the possibility that AI development could face greater constraints.

AI-related stocks fell sharply on Monday after the latest warnings. Nvidia, the world’s most valuable public company and one of the central suppliers of the computing infrastructure required to train and operate advanced AI models, fell 3% in premarket trading.

Intel, Micron and SK Hynix also dropped more than 5%.

The reaction illustrates the financial sensitivity of the AI ecosystem to assumptions about continued expansion. Nvidia’s business depends heavily on demand for accelerators used by AI developers and data-center operators. Memory manufacturers such as Micron and SK Hynix have also benefited from the enormous hardware requirements associated with AI infrastructure.

A meaningful slowdown in frontier model development could therefore affect much more than the laboratories themselves. It could ripple through semiconductor manufacturers, data-center operators, cloud providers, networking companies and the energy infrastructure being built to support AI computing.

That helps explain why Burry’s criticism has attracted attention. If the leading AI companies voluntarily slow development, the consequences would extend throughout an industry that has been built around the expectation of rapidly increasing compute demand.

Washington Wants The Opposite

The safety argument is also running into political pressure. President Donald Trump said over the weekend that “very negative forces” were behind what he described as apocalyptic discussions about AI. He said the worst outcome “won’t happen” and emphasized that the United States must beat China in the AI race. That puts Washington’s priorities in direct tension with the most cautious interpretation of Amodei’s proposal.

The U.S. government has strong incentives to preserve its lead over China in advanced AI, while American technology companies have billions of dollars invested in maintaining that lead. Slowing frontier development could reduce some safety risks, but it could also create opportunities for competitors to move ahead.

This is the central problem Burry is highlighting.

A voluntary slowdown only works as a competitive strategy if major players slow together. If OpenAI, Anthropic and other U.S. laboratories restrain themselves while rivals continue advancing, the companies that comply could surrender technological and commercial ground.

At the same time, if every company is encouraged to move as quickly as possible because of competitive pressure, safety research may struggle to keep pace with the capabilities being developed. The result is an uncomfortable conflict between two incentives: the incentive to move fast and capture the economic value of AI, and the incentive to avoid developing systems whose risks may eventually exceed the ability of their creators to control them.

Burry’s intervention adds another layer by questioning whether the companies making the warnings can be trusted to define the appropriate speed themselves. His record gives the argument additional weight among investors. He became famous for correctly betting against the U.S. housing market before the financial crisis and has spent much of the past year publicly criticizing the economics of the AI boom and highlighting what he sees as signs of overinvestment.

But his skepticism does not settle the underlying safety question. Whether current large language models can ultimately produce artificial general intelligence, whether more capable systems could become uncontrollable, and how likely an extinction scenario might be remain deeply contested questions.

What Burry has put squarely on the table is a different question: who benefits when the companies at the center of the AI race tell the world that the race itself needs to slow down?

That question will matter more if Anthropic and other frontier AI laboratories approach the public markets. Investors will have to assess not only the technological claims and safety risks, but also whether the industry’s warnings, growth projections, and competitive strategies are sometimes serving the same corporate interests.

Good Luck Tensorpool Founders at OpenAI – from Tekedia Capital

0
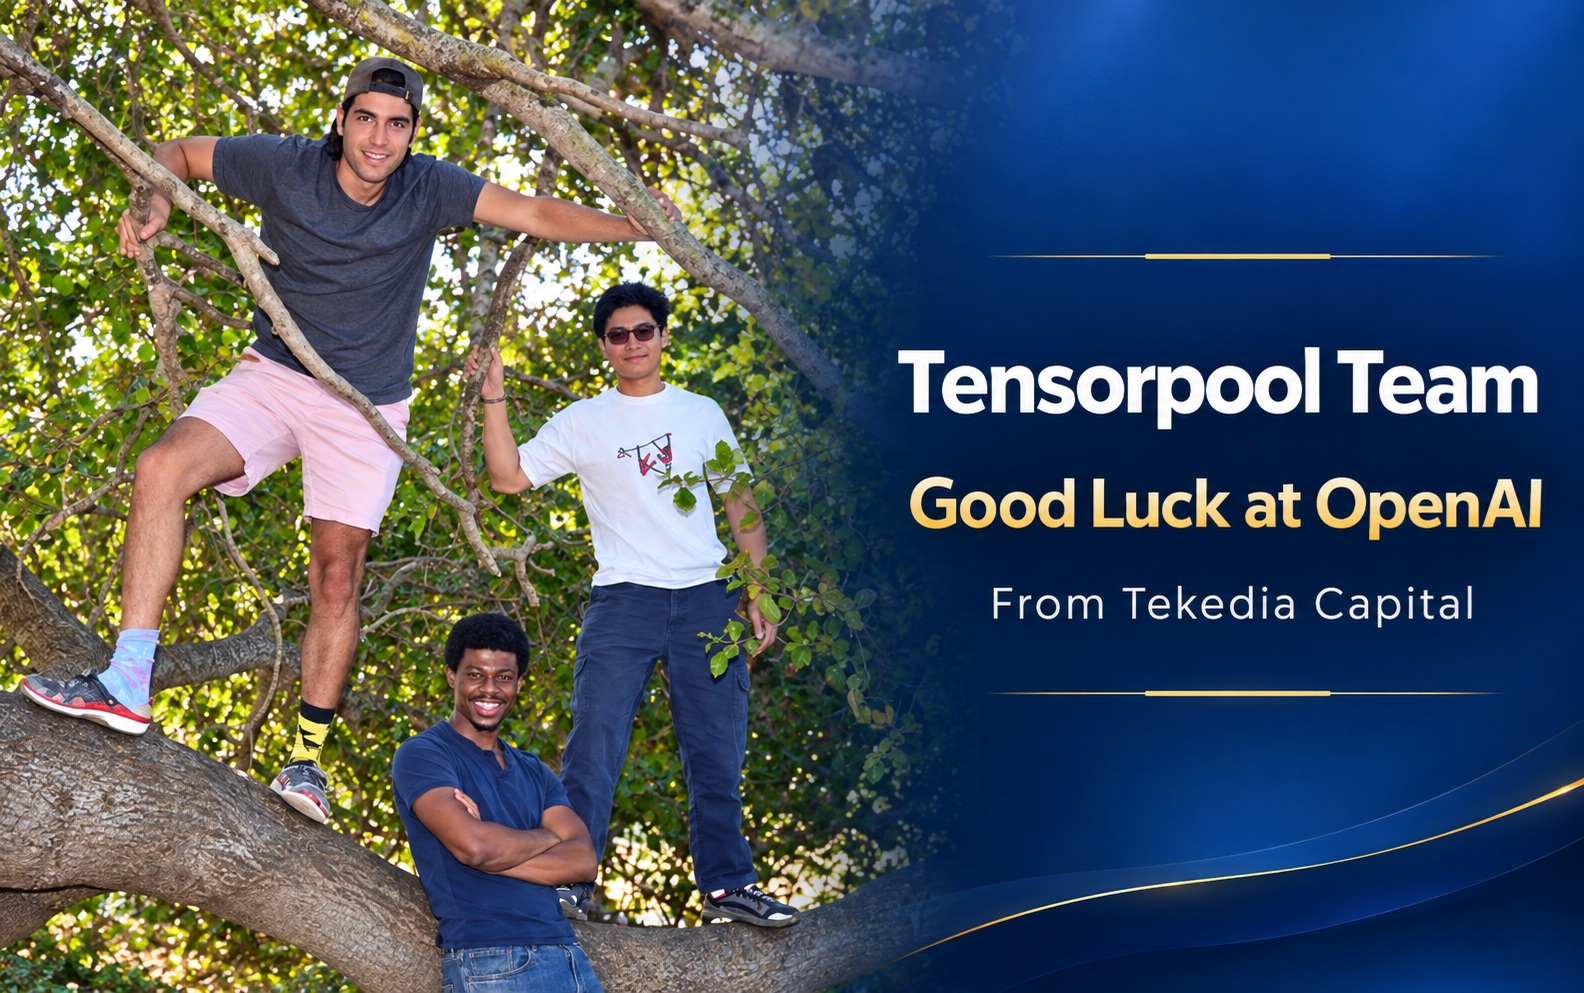
Tekedia Capital congratulates Joshua Martinez, Hlumelo Notsheand Tycho Svoboda as they resume in OpenAI after the AI pioneer acquired their startup, Tensorpool, which Tekedia Capital invested in. We wish three of you more wins ahead.
 
Tekedia Capital >> we befriend great founders!