DD
MM
YYYY

PAGES

DD
MM
YYYY

spot_img

PAGES

Home Blog Page 17

BOJ Seen Raising Rates to 1.25% as Inflation and US Pressure Accelerate Japan’s Policy Shift

0

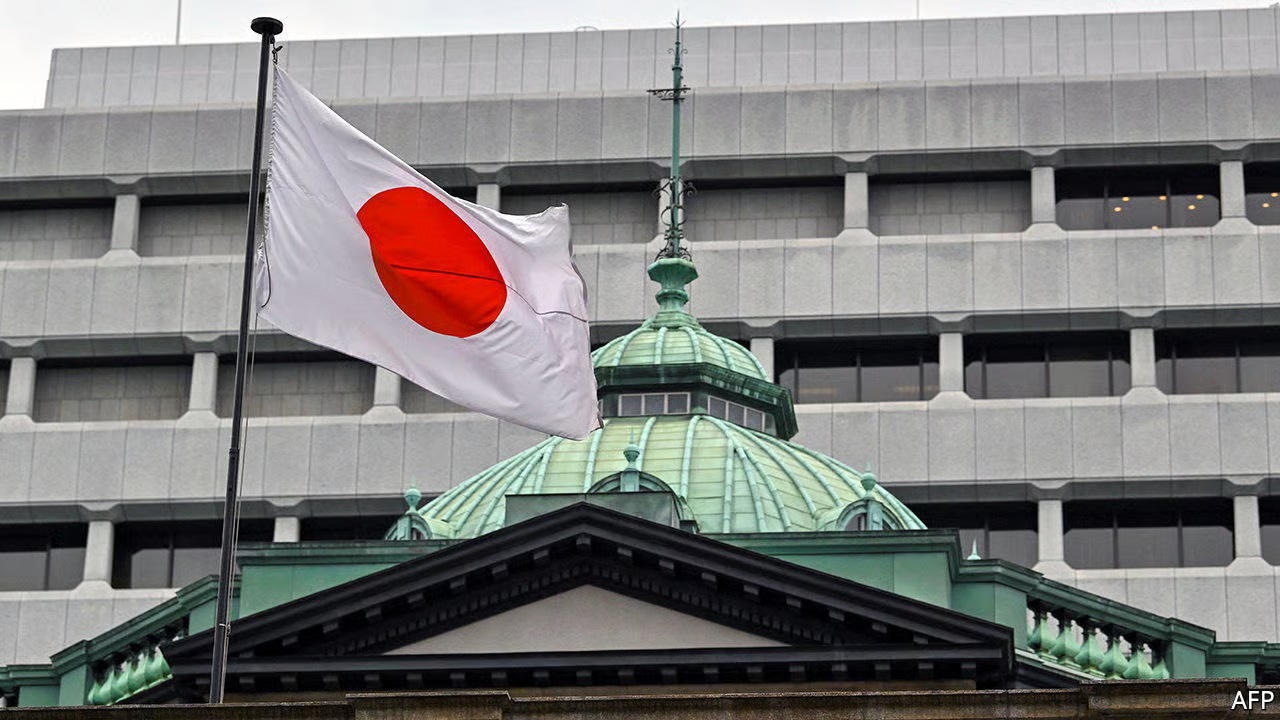
The Bank of Japan is expected to raise its policy rate to 1.25% on Friday, according to a CNBC survey, as persistent inflation, stronger wages and pressure from Washington increase the case for a faster withdrawal of Japan’s long-running monetary stimulus.

About 89% of the 18 economists and analysts surveyed by CNBC between Sept. 9 and 14 expect the BOJ to raise its benchmark rate by 25 basis points at the conclusion of its two-day meeting.

Such a move would represent more than another incremental rate increase. It would signal that the BOJ is becoming more comfortable accelerating the tightening cycle after maintaining roughly six-month intervals between increases since it began normalizing monetary policy in March 2024.

The central bank last raised rates in June.

The case for another increase has strengthened as inflation and wages have moved higher. Japan’s headline inflation rate reached 1.9% in July, its highest level this year, as energy costs rose amid the Iran war. Real wages also increased 2.4% in July, marking their seventh consecutive month of growth.

The combination is important for the BOJ because sustained wage gains provide a stronger foundation for inflation than temporary increases in energy prices alone. Policymakers have been seeking evidence that Japan can sustain a cycle in which higher wages support consumption and prices, allowing monetary policy to move further away from the ultra-loose settings that defined the country’s economy for years.

The timing is also being shaped by Washington.

Washington Wants a Stronger Yen

The Trump administration has been vocal about the need for Japan to continue raising interest rates, putting Prime Minister Sanae Takaichi’s preference for easier monetary policy and expansionary fiscal policy under greater pressure.

Treasury Secretary Scott Bessent most recently urged BOJ Governor Kazuo Ueda to take “decisive market and monetary steps” at the G20 finance ministers and central bank governors meeting earlier this month.

The U.S. has an interest in a stronger yen partly because of its implications for global bond markets.

A persistently weak yen can increase pressure on Japanese investors and authorities to support the currency. Japanese institutions hold large amounts of overseas assets, including U.S. Treasurys, and a sharp yen decline could create incentives to sell some foreign assets and bring funds home. That could put additional upward pressure on U.S. Treasury yields at a time when long-term borrowing costs are already elevated.

The currency issue has already moved beyond rhetoric. Japan and the United States conducted a joint intervention in late July aimed at strengthening the yen, marking a significant step in efforts to stabilize the currency.

“The Trump administration has effectively checked any potential move by a Takaichi administration to block the Bank of Japan from raising interest rates,” said Takahide Kiuchi, executive economist at Nomura Research Institute and a former BOJ policy board member.

“Consequently, the Bank of Japan has gained a free hand to proceed with rate hikes,” he said.

That does not mean Washington controls Japanese monetary policy. The BOJ remains responsible for setting rates, and domestic inflation, wages, economic activity and financial conditions remain the formal basis for its decisions. But the interaction between monetary policy and exchange rates has become difficult to separate from the broader U.S.-Japan economic relationship.

Recent comments from BOJ board members have also taken a hawkish tone, leaving open the possibility that the central bank could move more quickly than previously expected.

Economists Split on How Fast the BOJ Should Move

The survey nevertheless shows that the path beyond Friday remains uncertain.

Jesper Koll, expert director at Monex Group, is the most aggressive outlier. He expects the BOJ to deliver a 50-basis-point increase in a “one and done” move, rather than the conventional 25-basis-point increase.

Carlos Casanova, senior economist for Asia at UBP, takes the opposite view. He expects the BOJ to leave rates unchanged for now, although he believes the central bank is already behind the curve and eventually expects two 25-basis-point increases every six months.

“Data doesn’t yet support a regime shift,” Casanova said, arguing there is “insufficient visibility to justify a faster pace of rate hikes.”

Iran tensions and oil prices remain his main concern, since a sustained energy shock could raise headline inflation while simultaneously weakening household purchasing power and economic activity.

Higher inflation caused by stronger domestic demand and wages gives policymakers more reason to tighten. Inflation driven primarily by imported energy costs is more difficult because rate increases cannot directly reduce oil prices and could further weaken economic activity.

The composition of the inflation increase will therefore remain important as the central bank determines whether higher prices represent a durable shift in Japan’s inflation regime or another external shock.

Political appointments could also make Friday’s meeting more contentious.

Around one-third of survey respondents identified Toichiro Asada and Ayano Sato as the BOJ board members most likely to dissent if the central bank raises rates. Both are viewed as reflationists and were appointed by Takaichi earlier this year.

Their positions could matter more if the government seeks to balance expansionary fiscal policy with tighter monetary conditions. A stronger fiscal push could support demand and wages while simultaneously making it more difficult for the BOJ to justify maintaining very low interest rates.

Yen Faces Its Own Policy Test

The yen is likely to be the most immediate market indicator of how investors interpret the BOJ’s decision. About 61% of respondents expect the currency to trade between 155 and 160 against the dollar over the next month.

A rate increase should, in principle, narrow the interest-rate gap between Japan and the United States and provide support for the yen. But the currency’s reaction will depend heavily on what the BOJ signals about subsequent increases.

A 25-basis-point hike accompanied by cautious guidance could produce a limited response if markets have already priced it in. A stronger indication that the central bank intends to accelerate normalization could generate a more substantial repricing of Japanese assets and the yen.

Homin Lee, senior macro strategist at Lombard Odier, expects the BOJ’s hawkish shift to help keep the yen below 160 per dollar. But he does not expect further appreciation to come easily.

A move through 150 would be difficult, he said, because government and business officials would push back against what they regard as “inappropriately” rapid appreciation, creating an unusual policy tension. The United States wants a stronger yen partly to reduce external imbalances and limit risks to U.S. bond markets, while Japanese policymakers and exporters have historically been sensitive to the economic effects of rapid currency appreciation.

For global investors, the BOJ decision extends well beyond Japan.

A faster tightening cycle could change the attractiveness of Japanese bonds relative to overseas assets, influence the behavior of Japanese institutional investors, and affect global funding markets. If Japanese investors repatriate capital as domestic yields rise, the effects could reach U.S. Treasurys and other major bond markets.
OpenAI Taps Telon to Bring Advanced AI Workflows to Lawyers and Legal Teams

0

OpenAI’s latest move into the legal sector signals a shift in how enterprise AI may be deployed: rather than simply giving lawyers access to powerful models, the company is building an ecosystem around implementation, training and workflow integration.

Its newly announced partnership with London-based startup Telon illustrates that strategy. Telon, founded in June 2026 by former trial attorney Lewis Bretts, specializes in what it calls “legal engineers.”

These professionals are primarily former lawyers who help law firms and corporate legal departments configure AI systems, develop prompts and agents, and train employees to use the technology effectively.

OpenAI has designated Telon a “select partner,” bringing the startup into its broader Partner Network. The significance of the arrangement lies in the problem it attempts to solve. Artificial intelligence has already demonstrated its usefulness for legal research, document analysis, drafting and other knowledge-intensive tasks.

Yet purchasing an AI subscription does not automatically transform a law firm’s workflow. Lawyers still need to understand how to structure requests, evaluate outputs, integrate AI into existing systems and maintain appropriate human oversight.

That implementation gap is becoming an important battleground in enterprise AI. OpenAI’s own work with law firms illustrates the opportunity.

Australian firm Gilbert + Tobin has reported using ChatGPT and Codex across its operations, reducing some recruitment research and data-extraction work from roughly four hours to 20 minutes and cutting selected conflict, KYC and AML checks to about five minutes.

The firm says governance and human accountability remain central to its deployment. OpenAI has also collaborated with Willkie Farr & Gallagher on firmwide AI adoption and the development of proprietary AI platforms through the firm’s innovation organization.

These examples suggest that the legal market is moving beyond experimentation toward deeper integration of generative AI into professional workflows. Telon’s model adds another layer. Instead of building another standalone legal AI application.

It positions people with legal expertise between the technology and the organizations using it. That approach could prove important because legal work carries unusually high requirements for accuracy, confidentiality and professional judgment.

A lawyer cannot simply accept an AI-generated answer because it sounds convincing. Legal conclusions must be supported by authoritative sources, relevant facts and applicable law. Errors can create financial, regulatory and reputational consequences.

The human lawyer therefore remains responsible for judgment even when AI performs much of the preliminary work.

This makes the “legal engineer” potentially more than a technical consultant. The role sits at the intersection of legal practice, software engineering and AI workflow design.

The partnership represents a way to scale specialized expertise without building every industry-specific implementation capability internally. The company launched its Partner Network in June, with a broader goal of enabling consultants and partners to deploy its technology inside organizations.

The legal industry is already crowded with specialized AI providers, including companies such as Harvey and other legal technology firms. Reuters reported earlier this year that AI companies were increasingly competing for law firms and even law students as the next generation of legal professionals becomes an important customer base.

The emerging competition is therefore not simply about whose model is most capable. It is increasingly about who can make AI reliable, usable and deeply embedded in professional environments. OpenAI’s partnership with Telon points toward that next phase.

The future of AI in law may depend less on replacing lawyers than on redesigning how lawyers work—with AI handling increasingly complex tasks while human professionals retain responsibility for interpretation, strategy and accountability.

Why Cloud Security Is Essential for Business Digital Transformation

0

A mid-sized firm can move customer portals, analytics workloads, and development environments to the cloud within months. But its security operating model rarely changes at the same speed, and this gap is where digital transformation begins to carry more risk than the board expected.

That’s why cloud security matters because transformation expands the number of identities, applications, data stores, and connections that security teams must track. Protecting that expansion without turning every release, acquisition, or migration into a fresh security project requires a clear operating model.

Cloud Adoption Changes the Shape of Business Risk

Cloud migration isn’t merely a change in hosting location. It changes who can access business systems, how applications communicate, and which teams can build infrastructure. Therefore, understanding cloud security for digital businesses gives technology and security leaders a useful starting point for examining these changes.

But it’s also messy. A developer may deploy a storage service for a short-lived project, but a business unit connects a new software platform without involving the SOC. Neither action looks alarming on its own; however, six months later, the organization has sensitive data spread across several services, inconsistent access controls, and no agreed owner for half the alerts.

Shared Responsibility Still Leaves Work for the Customer

Cloud providers protect their underlying infrastructure, but customers remain responsible for identities, data, configurations, and application behavior. The exact boundary changes between infrastructure, platform, and software services.

The UK National Cyber Security Centre’s shared responsibility guidance recommends understanding which security duties remain with the customer for each service and deployment model.

This may sound obvious, but incident reviews suggest otherwise. Teams often discover too late that nobody was monitoring privileged access, checking public exposure or testing whether backups could be restored outside the affected account.

Why Digital Transformation Depends on Cloud Security

Transformation programs are judged by business movement: shorter release cycles, faster market entry, lower operating friction and better use of data. Security needs to support those outcomes, not sit beside them as a separate technical function.

It Keeps Rapid Change from Creating Hidden Exposure

Cloud environments can change hundreds of times in a day. New workloads appear, permissions are edited, and services connect through APIs. A quarterly configuration review can’t keep pace with that rate of movement.

That’s why security teams need continuous visibility into assets, identities, data flows and configuration changes. The hard part isn’t collecting more alerts; it’s finding the few changes that create a credible route to sensitive data or critical operations.

Context matters because an exposed test system with synthetic data doesn’t carry the same risk as an exposed administrative interface connected to a production database. Treating both as equal wastes time.

It Protects the Identities Behind Cloud Activity

In traditional networks, defenders could place considerable trust in location. But cloud services have weakened that assumption because employees, contractors, applications, and automated workloads may connect from almost anywhere.

That’s why in this system, identity becomes the practical control point. So, businesses and cloud security operators should start with phishing-resistant authentication for privileged roles, short-lived credentials for workloads, and tightly scoped permissions.

After that, focus on removing dormant accounts, while emergency access accounts need separate monitoring and regular tests. Service identities also deserve the same scrutiny as human administrators, sometimes more, since they’re easily forgotten and may hold broad permissions.

It Makes Compliance Evidence Easier to Produce

Regulators and customers don’t accept “the provider handles security” as sufficient evidence. Organizations need to show where regulated data is stored, who can access it, how long logs are retained, and what happens when a supplier or region becomes unavailable.

The European Union Agency for Cybersecurity offers a cloud security risk and procurement guide that links cloud risks with questions organizations can ask providers. Although written for smaller businesses, the procurement logic scales well: get evidence, clarify contractual duties, and examine exit conditions before moving important workloads.

Good cloud security also creates an auditable trail as part of normal operations. That’s far better than assembling screenshots and spreadsheets a week before an assessment.

It Gives Incident Responders Something They Can Actually Use

Cloud incidents are different from conventional endpoint compromises. An attacker may misuse a valid token, change a policy, create a new access key, and copy data through an approved service, and that’s why standard malware alerts never appear.

So the question is: Can the SOC reconstruct that activity quickly? If the answer is “probably”, the organization isn’t ready.

Useful preparation includes centralized control-plane logs, synchronized timestamps, protected log storage, and tested procedures for revoking sessions. Responders also need access to cloud administrators who understand the affected environment.

A Practical Cloud Security Framework for Transformation Teams

Security works best when it’s built into the transformation plan before workloads move. Here, the following five questions can expose most early weaknesses:

  1. What are we moving? Record the data, applications, dependencies, and business owners.
  2. Who can access it? Include administrators, developers, suppliers, service accounts, and automated pipelines.
  3. Which controls are native to the service? Use managed security capabilities where they meet the requirement rather than rebuilding familiar data-center patterns.
  4. What must the SOC be able to see? Define mandatory logs, retention periods, alert routes, and escalation owners.
  5. How will we recover or leave? Test restoration, account isolation, and data portability before a crisis forces the question.

Measure Exposure, Not Security Activity

Counting blocked events or generated alerts says little about business risk. Better cloud security measures include the number of privileged identities without strong authentication, internet-facing assets with known weaknesses, unencrypted sensitive stores, and critical workloads without a tested recovery path.

Time also matters, which is why you should track how long high-risk misconfigurations remain open and how quickly you can revoke access across cloud services during an incident.

Cloud Security Lets Transformation Move Without Losing Control

Digital transformation creates value by allowing organizations to change faster. Yet speed becomes expensive when nobody can explain where sensitive data sits, which identities control it, or how the business would recover after an account takeover.

Cloud security provides that missing discipline. It connects architecture, identity, monitoring, compliance, and recovery to the transformation program itself, instead of adding controls after deployment. The goal isn’t to eliminate every technical risk- that won’t happen but to keep them visible, owned, and within the organization’s tolerance while the business continues to build.

How a Security Operation Centre Strengthens Digital Business Resilience

0

A retailer’s payment platform begins generating unusual authentication traffic late on Friday. Nothing has failed yet, customers are still checking out, and the infrastructure team sees no obvious outage.

But somewhere between those signals and the next board update, the business may be heading towards fraud, data loss, or days of disrupted trading.

A Security Operation Centre gives the enterprise a coordinated way to detect that shift, judge its business significance, and contain the damage before a technical event becomes an operational crisis. Its value isn’t confined to monitoring.

Done well, it connects security decisions with service continuity, regulatory duties, customer trust, and recovery priorities.

Resilience Depends on Decisions, Not Dashboards

Security teams rarely suffer from a total absence of data. The usual problem is fragmentation. Network telemetry sits in one system, endpoint alerts in another, cloud activity somewhere else, while identity events arrive without enough context to show whether an account belongs to an intern or the finance director.

A modern Security Operation Centre framework brings those signals into an operating model built around monitoring, investigation, response, recovery, and continued refinement.

The technology matters, of course. Yet the real test is whether analysts can turn scattered evidence into a sound decision while the clock is running.

It Connects Technical Activity to Business Impact

An alert marked “critical” by a security product isn’t automatically the organisation’s most urgent problem. A medium-severity identity anomaly affecting a privileged administrator may carry far greater business risk than malware found on an isolated test machine.

Mature teams add context before assigning priority:

  • Which business service is involved?
  • Does the affected identity have privileged access?
  • Is regulated or commercially sensitive data exposed?
  • Could containment interrupt revenue or customer access?
  • Who owns the recovery decision?
  • Is legal, regulatory, or executive notification required?

This changes the discussion. Analysts stop treating every signal as an isolated technical object and start asking what failure would mean for the business.

Faster Detection Shrinks the Damage Window

Most incidents don’t begin with a cinematic system failure. They start quietly: an unusual login, a newly created account, a suspicious process, or a small outbound data transfer that looks harmless without supporting evidence.

The Security Operation Centre looks for relationships between those events. A questionable login becomes more serious when it’s followed by mailbox rule changes, privilege escalation, and access to a sensitive cloud repository. Correlation gives the team a story, even if the first chapter looked routine.

Speed still isn’t the only measure. A hurried but poorly judged response can cut off a customer platform, erase useful forensic evidence, or alert an intruder before the team understands the intrusion path.

Good Triage Protects Analyst Attention

What should happen when thousands of alerts arrive each day?

Not every alert deserves a human investigation. Known false positives should be tuned out, repetitive low-risk actions can be automated, and cases with credible business impact should move quickly to experienced analysts. That sounds obvious. In practice, tuning often slips behind project work until noise becomes normal.

A workable triage model should consider confidence, asset value, user privilege, exposure, and potential blast radius. Analysts also need permission to challenge the default severity assigned by a tool. Context beats colour coding.

Response Must Be Designed Before the Incident

Incident response isn’t a document that sits on a shared drive until audit season. It’s a set of decisions teams have already discussed, tested, and refined before pressure arrives.

Can the SOC isolate an executive laptop without waiting for multiple approvals? Who has the authority to temporarily suspend a revenue-generating application? If ransomware spreads across a shared environment, which services come back first? Questions like these reveal the gap between having a response plan and being genuinely prepared to execute it.

Guidance from the Centre for Internet Security (CIS) emphasizes that effective incident response depends on preparation, clearly defined roles, asset visibility, communication workflows, and coordinated recovery activities rather than technology alone.

That reflects how real incidents unfold. Detection is only one piece of the puzzle. Preparation, governance, business alignment, stakeholder communication, and recovery planning often determine whether an incident becomes a short disruption or a prolonged operational crisis.

Use Playbooks, but Leave Room for Judgement

Playbooks reduce hesitation during familiar events such as credential theft, malware detection, cloud account compromise, or suspected data exfiltration. They should define evidence to collect, containment options, escalation paths, communication triggers, and recovery checks.

Still, no playbook survives first contact unchanged.

Consider a mid-size financial services firm migrating workloads to a hybrid environment. Isolating a compromised server may be technically simple, yet doing so could interrupt payment processing or remove evidence needed for regulatory review. The analyst needs a decision path, not just an automated button.

Tabletop exercises help uncover those conflicts before a real incident. They also reveal outdated contact lists, unclear ownership, unavailable backups, and dependencies nobody documented.

Recovery Is Where Resilience Becomes Visible

Containment stops immediate harm. Recovery decides whether the organisation can return to normal without reopening the same weakness.

The SOC should work with infrastructure, application, identity, legal, communications, and business teams to validate recovery. That means checking restored systems, rotating exposed credentials, monitoring for renewed activity, and confirming that critical services behave as expected.

The work continues after systems come back.

A useful post-incident review asks what delayed detection, which controls failed, where teams lost time, and whether the original business impact estimate was accurate. Findings should lead to owned actions with dates. Otherwise, lessons learned become minutes from a meeting nobody revisits.

For regulated organisations, this operational discipline also supports accountability. Tekedia’s overview of cybersecurity guidelines for Nigerian financial institutions reflects the close relationship between cyber risk management, operational stability, and public confidence.

Measure Outcomes the Board Can Use

Alert totals make busy dashboards, but they say little about resilience. Leaders need measures tied to exposure and interruption.

Useful indicators include:

  • Time taken to validate a credible incident
  • Time from validation to containment
  • Percentage of critical assets with usable telemetry
  • Repeat incidents caused by unresolved root issues
  • Recovery time for priority business services
  • Playbook performance during exercises and live cases
  • High-risk access or asset gaps awaiting remediation

These figures won’t answer every board question. They do, however, show whether the organisation is getting quicker, sharper, and less likely to repeat an expensive mistake.

Digital Resilience Is an Operating Habit

A Security Operation Centre strengthens digital business resilience when it helps the organisation make better decisions under pressure. That requires visibility, skilled investigation, rehearsed authority, credible recovery plans, and honest review after the event.

The strongest SOC isn’t necessarily the one with the most screens or the largest alert queue. It’s the one that can recognise a developing problem, explain what the business stands to lose, act without confusion, and help critical operations return safely. Cyber incidents will still happen. Whether they become prolonged business failures is a different question.

UK Workers Spend Nearly £1 Billion a Year on AI Tools for Their Jobs – Deloitte

0

One in six workers in Britain is paying out of their own pocket for an artificial intelligence tool to help with their job, collectively spending nearly £1 billion ($1.4 billion) a year, according to research published by Deloitte on Wednesday.

The findings point to a widening gap between how quickly employees are adopting generative AI and how quickly employers are making the technology available in the workplace. Rather than waiting for companies to approve or provide AI tools, a significant share of workers are turning to services such as ChatGPT, Claude, Google Gemini and Microsoft Copilot themselves.

Deloitte’s inaugural GenAI Workforce Survey found that about two-thirds of workers had used generative AI tools, while nearly a quarter were using them every day as part of their jobs. More than three in 10 respondents, or 31%, said they were using AI without their employers’ knowledge, a practice commonly referred to as “shadow AI.”

At the same time, 17% said they were personally paying for at least one generative AI tool for work.

“UK workers are showing they don’t want to wait for permission to use GenAI,” said Hayley McKelvey, Deloitte UK’s chief AI officer.

“Many are already using free tools or pay for premium versions themselves to help them get work done.”

The scale of employee-funded adoption suggests that generative AI is no longer confined to formal corporate technology programmes. Workers are increasingly treating AI assistants as ordinary productivity tools, even where their employers have not established an approved platform, policy or budget for their use.

The development has yielded a new set of questions for companies around data protection, intellectual property, security and accountability. When employees independently select AI services, organizations may have less visibility over what information is being entered into those systems and how the tools are being used.

The survey found that the most common workplace applications remain relatively straightforward. Workers primarily use AI to search for information, draft emails, and produce summaries. Those activities nevertheless generated measurable time savings. Respondents estimated that generative AI saved them an average of 70 minutes a week.

Deloitte partner Paul Lee said generative AI had rapidly become part of everyday working life, but its use remained concentrated on relatively basic tasks.

“Yet for many workers its role remains relatively basic, focused on searching for information and drafting content rather than supporting more complex work,” Lee said.

Companies have been assessing whether their growing AI investments are producing meaningful productivity gains. Widespread access to a chatbot can make individual tasks faster, but the larger economic opportunity may depend on whether businesses redesign workflows around AI rather than simply give employees another software application.

“The organizations that gain the greatest advantage from AI will be those that move beyond simply providing access to tools and focus on helping people use them with the appropriate guardrails and purpose,” Lee said.

The survey therefore captures two parallel developments. Employees are already integrating AI into their daily routines, while many organizations are still working out how the technology should be deployed, governed and connected to more complex business processes.

The £1 billion annual spending estimate also reveals an unusual feature of the current AI adoption cycle: part of the cost is being absorbed directly by workers.

Paying for a premium AI subscription, for employees, can be a relatively simple way to gain access to more capable models or additional features. However, widespread unofficial use can make it harder to determine which AI tools are being used, what value they generate and what risks they introduce.

The survey was conducted by Ipsos for Deloitte and covered 25,000 workers, giving the findings a broad view of how generative AI is entering Britain’s workplaces.

The data suggest that the next stage of workplace AI adoption may be less about persuading employees to use the technology and more about bringing existing usage into formal company systems. The challenge for employers is to turn what is currently a largely employee-driven experiment into controlled and purposeful use without removing the productivity gains that encouraged workers to adopt the tools in the first place.